Author: Protegrity
-
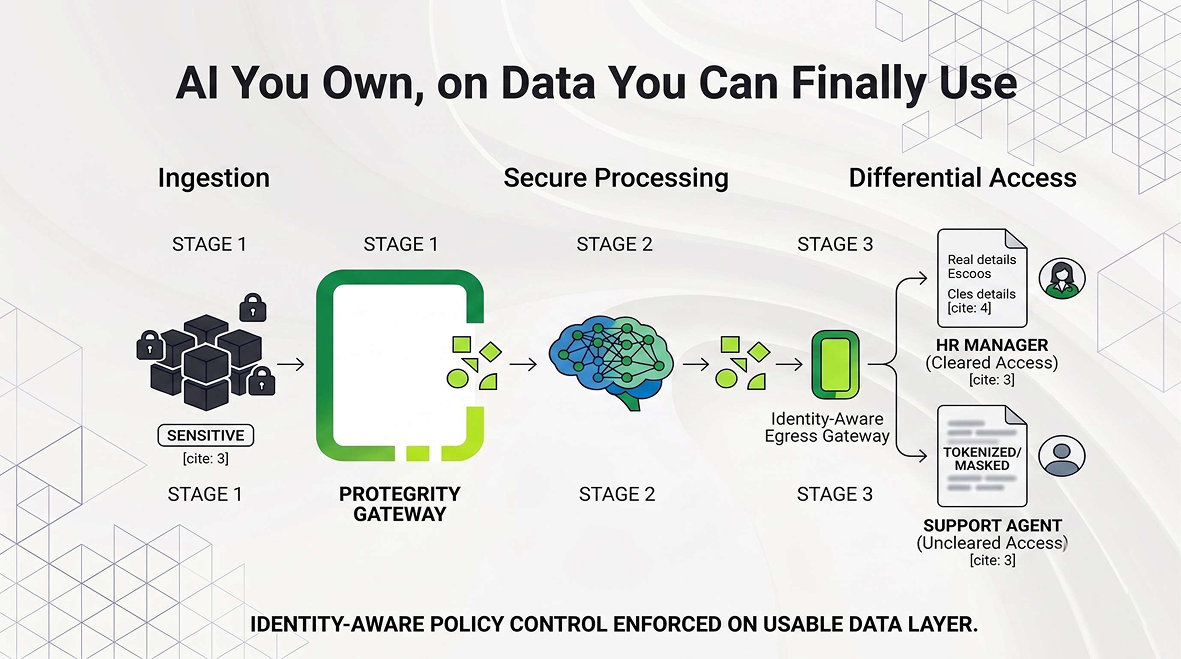
AI You Own, on Data You Can Finally Use
See how Protegrity and OpenTeams make sensitive enterprise data usable for sovereign AI. By protecting data at landing and using identity-based clearance to control when clear values are revealed, organizations can run analytics, models, and agents on governed data without exposing original identities.
-
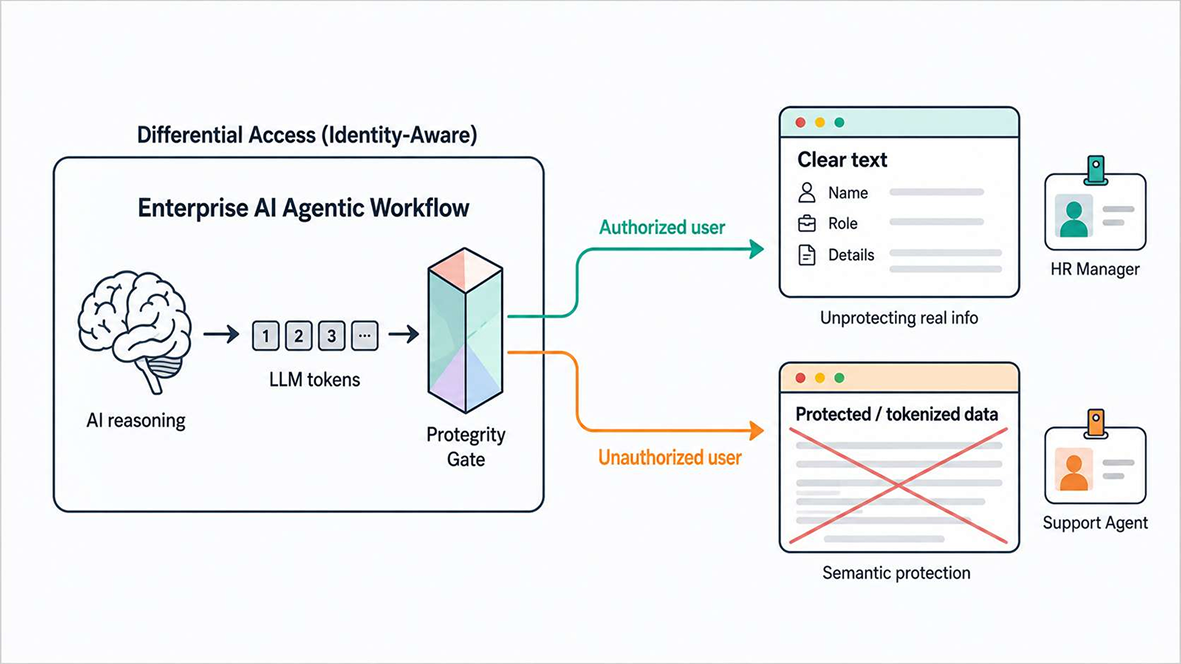
How Protegrity and Composio Secure Agentic AI Workflows
See how Protegrity and Composio protect sensitive data across agentic AI workflows using a “Privacy Sandwich” architecture. The approach applies tokenization before LLM processing and identity-aware policy at output, helping agents connect to enterprise applications while reducing exposure of PII, PHI, and PCI.
-
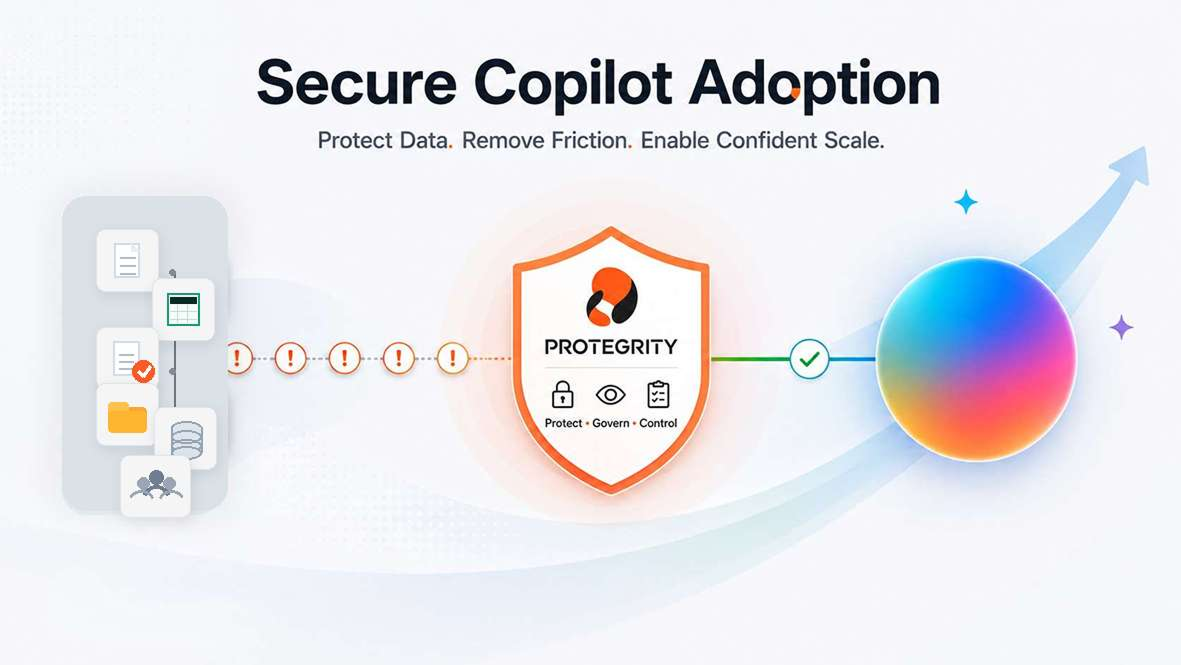
5 Reasons Microsoft Copilot Rollouts Stall and How to Fix Them
Learn why Microsoft 365 Copilot rollouts often stall when overshared content, outdated permissions, sensitive data sprawl, and fragmented governance leave enterprise knowledge unprepared for AI. Explore five practical steps for protecting data before Copilot indexes, retrieves, reasons over, or presents it.
-
-
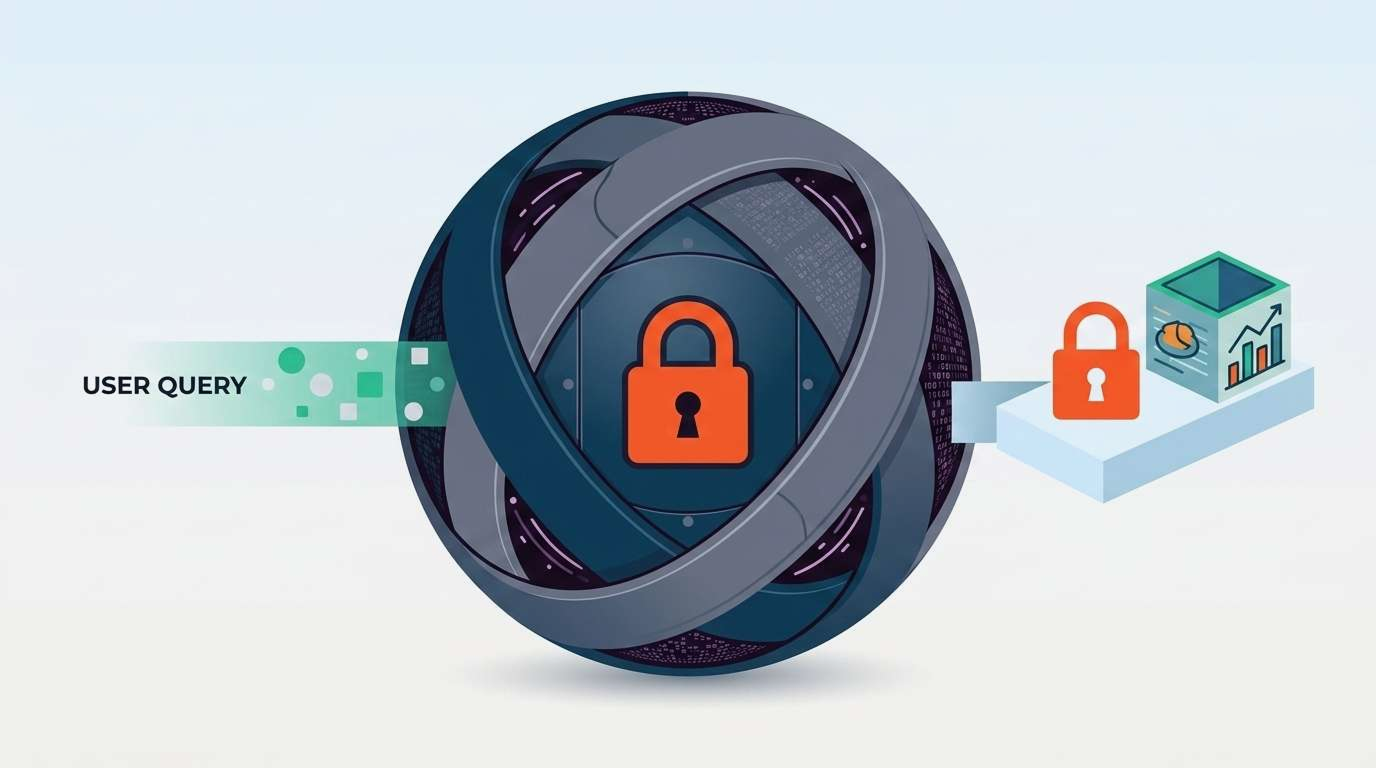
Ask Anything, Expose Nothing: Text-to-SQL Security
Defensible AI requires more than accurate outputs. Learn why regulated enterprises need data-layer protection to keep sensitive data usable, governed, and auditable across analytics, RAG, and agentic AI workflows.
-

-

How Do You Put a Price on Security and Compliance? Part III – Increasing Revenue
Protegrity helps enterprises reduce data friction so authorized teams can access and use sensitive data faster, without bypassing security or governance. By enabling trusted data access across AI, analytics, cloud, and cross-border workflows, organizations can accelerate time to value, support new revenue opportunities, and turn data protection into a driver of business growth.
-
-

-
